Survey
* Your assessment is very important for improving the work of artificial intelligence, which forms the content of this project
* Your assessment is very important for improving the work of artificial intelligence, which forms the content of this project
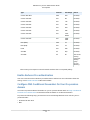
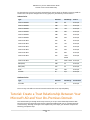
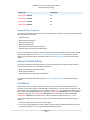
AWS Directory Service Administration Guide Manage Password Policies in Microsoft AD Max retries The number of times that communication with the RADIUS server is attempted. This must be a value between 0 and 10. Multi-factor authentication is available when the RADIUS Status changes to Enabled. Manage Fine-Grained Password Policies in Microsoft AD AWS Microsoft AD enables you to deï¬ne and assign diï¬erent password and account lockout policies (also referred to as ï¬ne-grained password policies) for groups of users you manage in your AWS Microsoft AD domain. For example, you can assign a less strict policy setting for employees that have access to low sensitivity information only. For senior managers who regularly access conï¬dential information you can apply more strict settings. AWS provides a set of ï¬ne-grained password policies in AWS Microsoft AD that you can conï¬gure and assign to your groups. To conï¬gure the policies, you can use standard Microsoft policy tools such as Active Directory Administrative Center (ADAC). To get started with the Microsoft policy tools, see Installing the Active Directory Administration Tools (p. 135). Topics ⢠Supported Policy Settings (p. 99) ⢠Delegate Who Can Manage Your Password Policies (p. 101) ⢠Assign Password Policies to Your Users (p. 101) Related AWS Security Blog Article ⢠How to Conï¬gure Even Stronger Password Policies to Help Meet Your Security Standards by Using AWS Directory Service for Microsoft AD Supported Policy Settings AWS Microsoft AD includes ï¬ve ï¬ne-grained policies with a non-editable precedence value. The policies have a number of properties you can conï¬gure to enforce the strength of passwords, and account lockout actions in the event of login failures. You can assign the policies to zero or more Active Directory groups. If an end-user is a member of multiple groups and receives more than one password policy, Active Directory enforces the policy with the lowest precedence value. AWS Pre-Deï¬ned Password Policies The following table lists the ï¬ve policies included in your AWS Microsoft AD directory and their assigned precedence value. Each policy has a name that begins with the domain name you speciï¬ed for your AWS Microsoft AD at the time you created your directory as shown. For more information, see Precedence (p. 100). Policy name Precedence <domainname>-PSO-01 10 Version 1.0 99